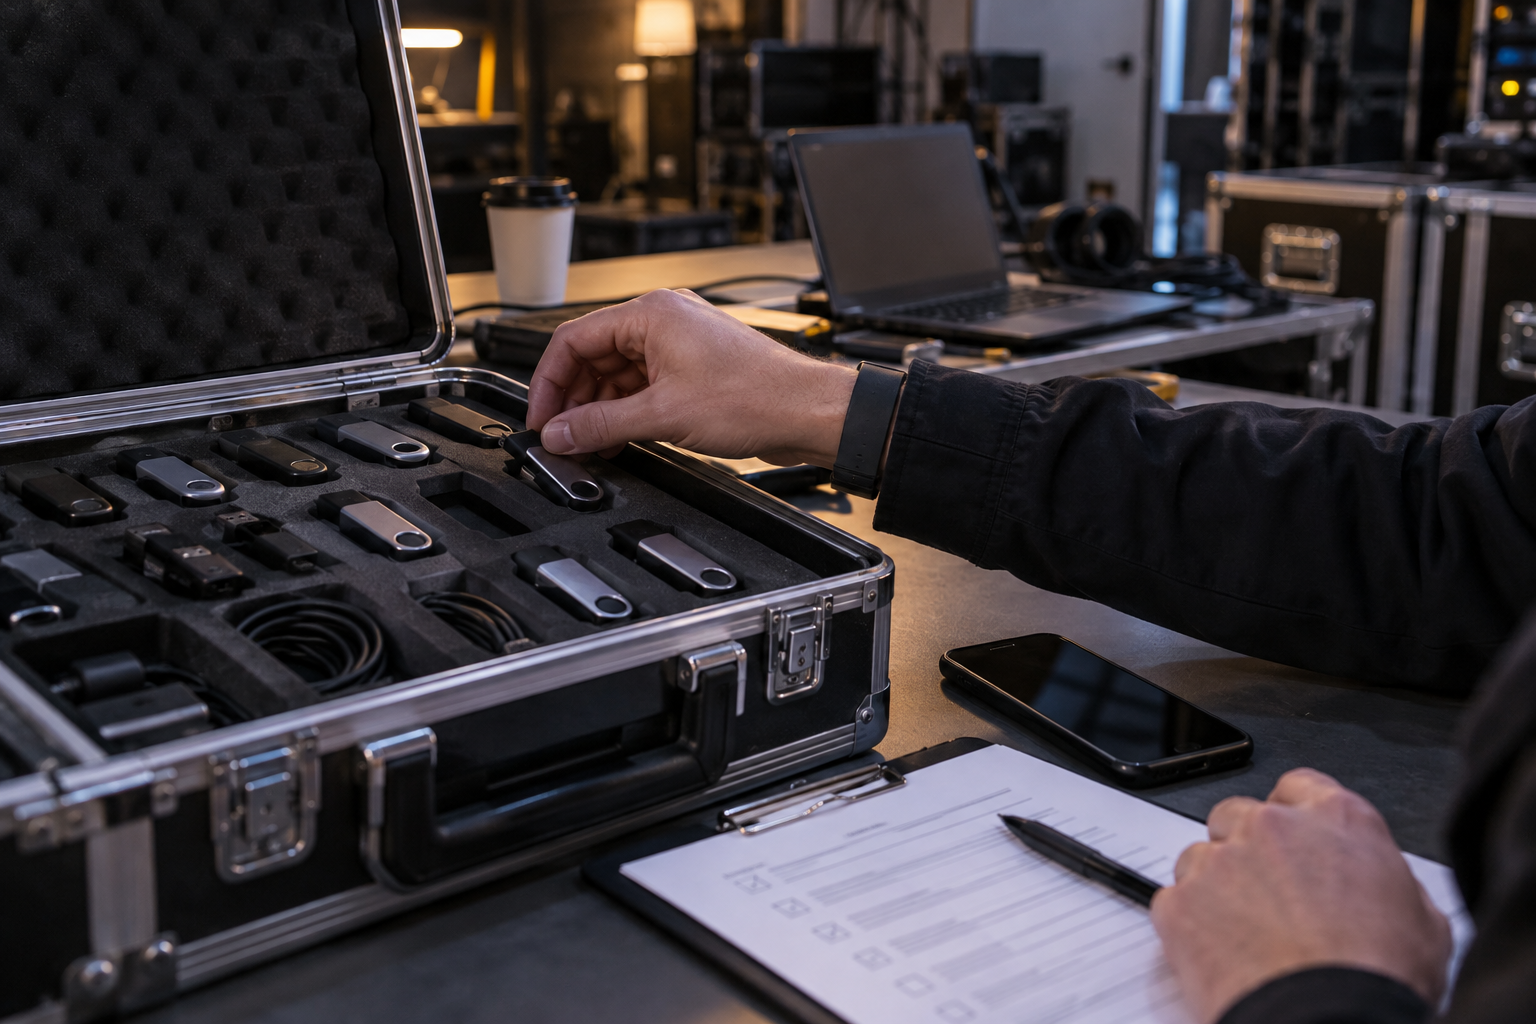
Treat loss as an incident, not a password test
Report the missing drive quickly, preserve the manifest and assess the data, protection state, password exposure, custody history and applicable contractual or legal duties. Do not promise that software protection makes a lost device harmless.
A drive is missing after load-out. The manager records the last verified custodian and time, freezes password sharing, retrieves the manifest, notifies the incident owner and supports a documented exposure decision while the team searches.
Run this control before handoff
- 01
Record when and where the drive was last verified.
- 02
Notify the event security and information owner through the incident route.
- 03
Retrieve the manifest, custody log and protection-test record.
- 04
Assess data sensitivity, secret exposure and recipient/device context.
- 05
Document search, containment, notification and replacement decisions.
Log the operational evidence
Record drive ID, last custodian/time/place, manifest, protection state, password route, search actions, exposure decision, notifications and closure.
Stop the handoff when
- Staff delay reporting while searching informally.
- The password travelled in the same case.
- No verified backup exists for operational continuity.
State the protection boundary
Do not equate with hardware-encrypted drives or untested Mac/Android compatibility. Password protection does not replace recipient authorization, endpoint policy, backup, recovery or physical chain of custody.
Event USB handoff questions
Is a protected lost drive automatically low risk?
No. Use the documented protection and exposure facts.
Should the password be changed?
Follow the product and incident plan; changing a separate account password may not alter existing drive data.
Sources for this decision
Links support specific boundaries and do not imply endorsement.